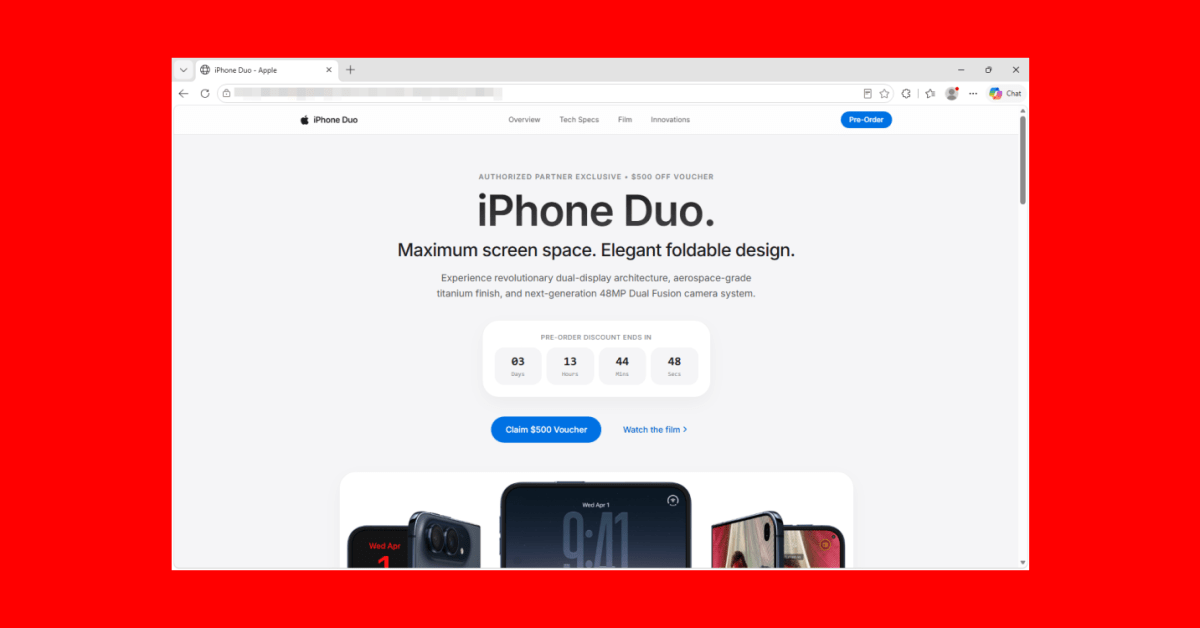
Scammers are luring users to a counterfeit iPhone Duo pre‑order site ahead of the official launch on Friday, October 16, hoping to steal their information.
The malicious page mimics the genuine Apple store closely and advertises a $500 voucher labeled an “Authorized Partner Exclusive”.
According to Malwarebytes researchers, the site leverages the DarkSword exploit chain, affecting certain unpatched older iPhones; merely loading the page triggers the attack—no interaction required.
Beneath its Apple‑like façade and the promised $500 discount, the page employs the leaked DarkSword exploit to compromise vulnerable iPhones. On success, a secondary payload harvests stored credentials, crypto‑wallet data, and Apple Notes. No form submission, download tap, or approval is needed—just opening the page initiates the exploit.
Once compromised, the malware gathers the device identifier and status, then tries to exfiltrate a list of installed apps and the contents of Apple Notes before shifting focus to cryptocurrency wallets.
The code scans for wallets such as MetaMask, Phantom, Trust Wallet, Coinbase Wallet, Exodus, and Tonkeeper, and also pulls saved credentials from the device’s keychain. When a targeted wallet is detected and initial contact with the command‑and‑control server succeeds, it uploads wallet files, harvested keychain data, and photo thumbnails—putting any exposed funds at risk.
Afterwards, it attempts to read messages, contacts, call logs, voicemail, email, calendar items, and cached location data, and can reach out to its server for additional commands.
Google disclosed the exploit chain in March, and Apple released a patch later that month.
Digitio’s Take
Standard precautions apply: avoid clicking unsolicited links unless you trust the sender and were expecting them, and keep iOS updated as soon as patches appear.
Screenshot: Malwarebytes